
Most Popular
Next-Gen Threat IntelligenceThreat Intelligence · 40.1B+ Records
Discover exposure
before threat actors do.
Real-time breach intelligence, automated stealer log correlation, 700+ social platform reconnaissance, and executive compliance reports.
No public compromise detected for this identity in indexed breaches.
Get started free
SOC 2 compliant · EU data residency · Instant activation
4.9 / 5.0
★★★★★
Security Analyst Rating
Zero query resale guarantee
End-to-end encrypted storage
Frankfurt & Dublin data centers
Comprehensive Intelligence
Engineered for security teams, fraud analysts and red teams
From one email or username, uncover complete digital identities, compromised credentials, and active threat exposure.
Deep Breach Indexing
Search through 40.1B+ records including stealer logs, database dumps, combos, and paste repositories with sub-second response.
Social Footprint Recon
Correlate usernames and pseudonyms across 700+ platforms, forums, developer networks, and instant messengers.
Algorithmic Risk Scoring
0–100 risk score weighted by credential recency, plain-text exposure, high-privilege access, and stealer telemetry.
Executive PDF Reports
Generate board-ready technical assessments, audit evidence, and investigation summaries in a single click.
Continuous Monitoring
Create automated monitors on company domains, executive emails, and VIP assets with instant webhook and email alerts.
Activity Chronograph
Track live Telegram presence and cross-platform activity to map 7x24 circadian heatmaps, isolate sleep routines, and deduce probable time zones.
Investigation Studio (Coming Soon)
Visual entity graph linking selectors, passwords, phone numbers, and addresses to map threat actor infrastructure.
Enterprise Privacy & 2FA
Zero query logs sold. TOTP two-factor security, session revocations, and complete data isolation.
Deep Breach Intelligence
Search 40.1B+ compromised records in milliseconds
Query multi-field breach entities across botnet stealer logs, database leaks, combo lists, and dark web paste drops. Recover plain-text passwords, salted hashes, and unexpired session tokens with sub-second response.
- Multi-field syntax: Email, Username, Phone, IP, Domain, and Password Hash
- Deep botnet telemetry: RedLine, Vidar, Lumma, and Racoon stealer archives
- Zero query logs sold or retained — privacy-first architecture
Relational Entity Forensics
Coming Soon
Uncover threat actor infrastructure with node & map graphing
Move beyond flat record lists. Investigation Studio automatically correlates selectors into dynamic node graphs, revealing hidden links between corporate identities, botnet C2 servers, cryptocurrency wallets, and physical IP geolocation coordinates.
- Recursive multi-hop pivoting across Depth 1, Depth 2, and Depth 3
- Dynamic force-directed topology and hierarchical tree layouts
- Integrated geospatial intelligence with IP coordinates & location clustering
Physical Geolocation & Network Attribution
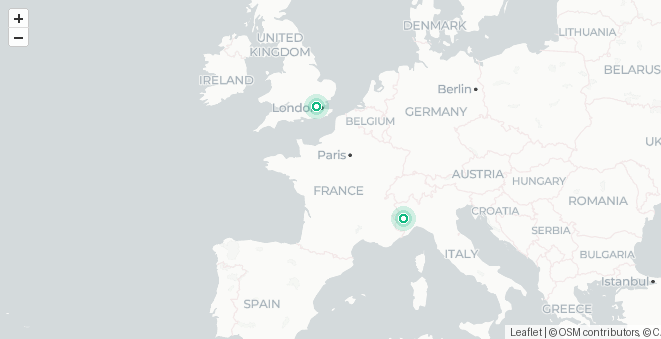
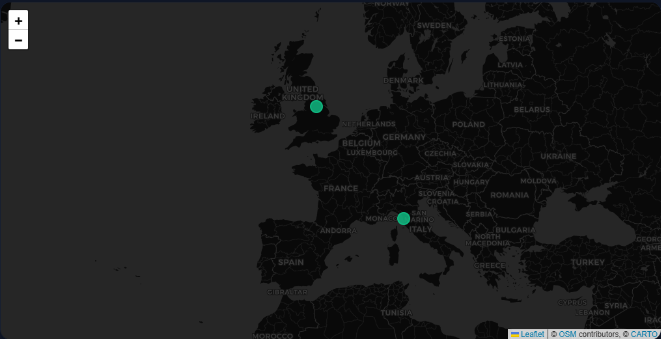
Triangulate threat infrastructure with live geospatial mapping
Pinpoint physical server locations, residential proxy exits, and threat actor IP clusters across the globe. Seamlessly cross-reference IP clusters with corporate breach exposures and ASN routing paths using CARTO high-precision basemaps.
- High-precision IP-to-city resolution with ISP & ASN network attribution
- Cluster correlation linking physical points directly to botnet telemetry and stealer logs
- CARTO basemaps with dynamic Positron light & Dark Matter themes, pin recentering, and telemetry
Operational Workflow
How DataStark delivers threat intelligence
Seamless integration between discovery, analysis, and executive reporting.
Ingest & Index
Continuous crawlers monitor public pastes, dark web marketplaces, and stealer distribution channels, deduplicating and indexing data in seconds.
Correlate & Enrich
Identities are automatically resolved across breach dumps and social networks, generating comprehensive link graphs and risk scores.
Remediate & Alert
Receive notifications immediately upon exposure and export audit-ready PDF reports for incident response and compliance.
Predictable Pricing
Transparent plans for teams of every size
Choose the tier that matches your intelligence scope. Instant crypto activation with verified threat intelligence.
Swipe to compare
Questions & Answers
Frequently Asked Questions
DataStark indexes 1,267+ distinct breach databases, botnet stealer logs (RedLine, Racoon, Vidar, Lumma), paste repositories, and public forums, encompassing more than 40.1 billion verified records updated every hour.
Yes. Queries are encrypted and tied strictly to your authenticated session. DataStark does not sell, license, or aggregate customer query logs for any third party.
We accept cryptocurrency payments processed through our secure automated gateway, supporting Bitcoin, Ethereum, USDT, Monero, Litecoin, Solana, and more. Direct card payments are not supported, ensuring privacy and secure digital settlements.
Yes. Paid tiers include instant one-click generation of executive PDF reports containing exposure timelines, risk scores, and technical details suitable for compliance reporting.
Start your investigation in seconds
Protect your organization, identify compromised credentials, and monitor threat actor reconnaissance with DataStark.